
Network location alone is not an adequate basis for trust.
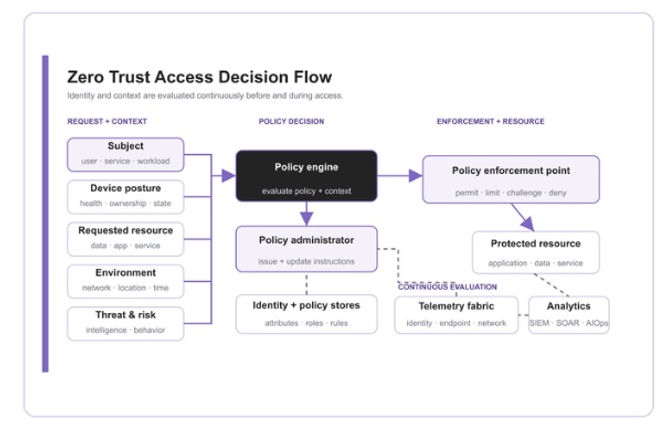
Zero Trust establishes a different model: access is evaluated using available identity, device, resource, environmental, and risk information; privileges are limited; policy is enforced close to the resource; and telemetry informs continued decisions. No single product creates that outcome.
HOW OSE CAN CONTRIBUTE
Potential OSE support includes:
-
Zero Trust current-state and maturity assessment
-
Mission, business, and security requirements
-
Target architecture and phased roadmap
-
Identity, authentication, and privileged-access integration
-
Device posture and endpoint-signal requirements
-
Policy-decision and enforcement architecture
-
Governance, operating model, and success measures
A PHASED APPROACH
Advance one use case at a time.
Understand
Identify resources, users, devices, workflows, dependencies, policies, and existing controls.
Prioritize
Select use cases where risk, mission, value, readiness, and measurable outcomes justify action.
Architect
Define the identity, network, application, data, policy, telemetry, and operational components.
Implement and Learn
Test the architecture, measure results, address gaps, and apply lessons to the next phase.